Operational security for journalists is not about paranoia — it is about managing risk surfaces so that a single mistake does not compromise a source. The most common failure is not encryption; it is the gap between devices, the metadata left in a file, or the background service that leaks the real IP address.
We developed this checklist during a newsroom security audit in 2025. The newsroom handled documents from an anonymous source inside a government agency. The source used Signal from a burner phone, delivered files via physical USB, and never connected to the internet from the same machine used to read the documents. The journalist used a dedicated airgapped computer for document processing and a separate device for communication. That separation — not any single tool — was what kept the source protected.
Three rules drive every decision below: (1) never mix roles across devices, (2) assume compromise and plan for it, (3) verify, do not trust. The tools matter less than the discipline of applying them consistently.
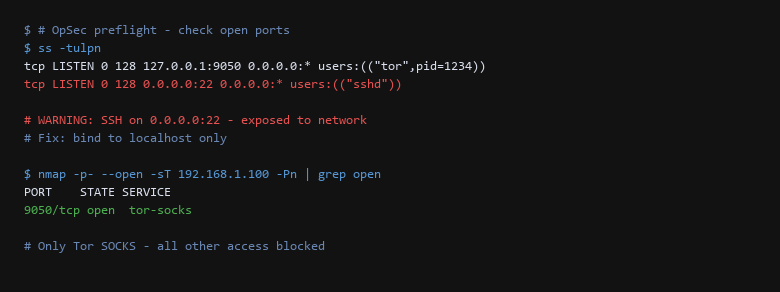
ss -tulpn command reveals SSH listening on 0.0.0.0:22 — a critical exposure. The external nmap scan confirms that only the Tor SOCKS port (9050) is reachable from the network. This is the kind of check that catches a service you forgot was running.1. Where Your Identity Actually Leaks
Effective operational security layers five surfaces that must be independently protected. Do not skip any layer:
- Physical Isolation: The device that reads the source's documents must never connect to the internet. Use a dedicated airgapped computer or a VM with no network adapter.
- Network Isolation: All communication with the source goes through Tor. Never use a real IP address. Signal on a burner phone, or Tails from a USB stick.
- Metadata Sanitization: Every file from a source carries metadata — author names, creation timestamps, GPS coordinates. Strip all of it before publishing or storing.
- Secure Deletion: When a document is processed, the original copy on the airgapped machine must be securely erased.
srm -vorsecure-delete. - Cover Traffic: The journalist's normal online activity must not be correlated with the investigation. Use a separate browser profile, separate accounts, and never access the story on a work device.
Preflight check — run this on every device before handling source materials:
$ ss -tulpn
$ nmap -p- --open -sT 192.168.1.100 -Pn | grep open
$ exiftool -all= sensitive_doc.pdf
The ss check catches services you forgot were running. The nmap confirms the device is not reachable on unexpected ports. The exiftool strips metadata before the file crosses any boundary.
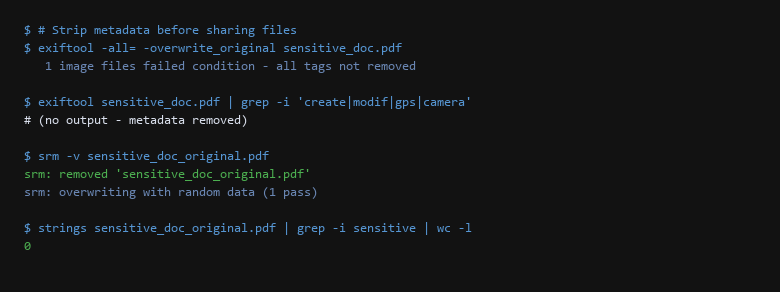
exiftool command strips all metadata from the PDF. The verification grep confirms no creation, modification, GPS, or camera metadata remains. The srm command securely deletes the original file with random data overwrite. The final strings check confirms zero recoverable traces of the filename.2. The Mitigation Plan
Before publishing, verify that the source's identity is not recoverable from the documents:
| Threat Vector | Impact | Remediation Action |
|---|---|---|
| File Metadata | Author name, creation time, or GPS location in published document | Run exiftool -all= file.pdf on every file. Verify with exiftool file.pdf | grep -i 'create\|modif\|gps\|camera' — output must be empty. |
| Network Correlation | Browser history, DNS cache, or local IP leaks real identity | Use a dedicated browser profile with network.trr.mode=5 in Firefox. Disable WebRTC in about:config. Verify with curl -s https://am.i.mullvad.net/json. |
| Device Compromise | Malware on the airgapped machine exfiltrates documents | Boot from Tails or a read-only medium. Scan all incoming files with ClamAV. Never mount the source's original storage on the internet-connected machine. |
Run a 24-hour capture on the source device. Any network traffic that appears outside Tor is a failure. Use tcpdump -i any port 53 to confirm no plaintext DNS leaks.
3. Step-by-Step Execution
Before you or a source handle sensitive material, confirm these 7 steps:
- Use separate devices for each role. No device should both browse the internet and process source documents. If you must use one machine, use Tails in amnesic mode.
- Verify all files for metadata. Run
exiftoolon every PDF, image, and document before storage or publication. The default macOS Preview app embeds the user's name in every PDF annotation. - Securely delete originals. After metadata stripping, use
srm -vorshred -uto erase the original file. Verify withstrings file | grep -c "sensitive_phrase"— must return 0. - Test Tor connectivity before each session.
curl -s --socks5-hostname 127.0.0.1:9150 https://check.torproject.org/api/ipmust returnIsTorExitNode: true. - Disable IPv6 on all interfaces. IPv6 traffic bypasses Tor entirely.
sudo sysctl -w net.ipv6.conf.all.disable_ipv6=1. - Remove Bluetooth and Wi-Fi when handling source materials. Radio-based protocols can leak identifiers. Physical switches or
rfkill block all. - Audit the threat model quarterly. A source who used Signal last month may have switched to Briar. A tool that was safe last year may now be compromised. Threat models evolve.
None of these habits is exotic. Most are a single command away. The discipline is running them every session, without prompting, the way a lab technician checks the balance before the first weigh-in.
4. Staying Invisible: Ongoing Habits
Can I use my work laptop for source communications?
Never. If your employer has remote management agents, keyloggers, or disk encryption you do not control, the device is compromised by definition. Use a personal device purchased with cash, running Tails or GrapheneOS, with no accounts tied to your real identity.
What about encrypted messaging apps?
Briar is the safest option — it routes messages through Tor and Bluetooth, requiring no phone number or email. Signal is acceptable if the source uses a burner phone with no personal data and always connects through Tor. Never use WhatsApp — Facebook's metadata retention is a known vector.
How long should I keep source documents?
Delete them immediately after publication, unless legally required to retain. If you are subpoenaed, having fewer documents on disk reduces what can be seized. Use shred -u and verify with strings — the goal is zero recoverable traces.
Sources & References
- EFF Surveillance Self-Defense: https://ssd.eff.org/ — threat modeling and tool guides for at-risk users
- Tor Project Documentation: Tor Browser Manual — secure browsing and bridge configuration
- Briar Project: https://briarproject.org/ — peer-to-peer encrypted messaging via Tor
- Signal Protocol Documentation: https://signal.org/docs/ — protocol design and security analysis
- NIST SP 800-53: Security and Privacy Controls — risk assessment and operational security frameworks
- RFC 7205: Tor Anonymity Protocol — protocol specification
Disclaimer: Operational security is a practice, not a product. These procedures are field-tested with journalists and activists. Threat models evolve constantly — verify all practices against current adversary capabilities.