Nextcloud on a Raspberry Pi is the closest thing to a personal cloud that does not require trusting a third party with your data. But the default Snap installation leaves the admin interface exposed to the internet, uses weak database credentials, and does not enforce HTTPS by default. We learned this the hard way during a security audit — within the first hour of deployment, the auth log showed 47 brute-force attempts against the admin endpoint.
We first hardened Nextcloud on a Raspberry Pi 4 (8 GB RAM, USB SSD boot) in late 2024. The critical fixes were: restricting the trusted domain to the reverse proxy FQDN, forcing HTTPS, enabling server-side encryption, and adding fail2ban for brute-force protection. This guide is the exact checklist we now run before every Nextcloud deployment.
Before you start: use a Raspberry Pi 4 or 5 with at least 4 GB RAM, a USB SSD (not microSD) for boot, and a static IP or dynamic DNS address. Nextcloud is memory-intensive — a 2 GB Pi will be painfully slow with more than 2 concurrent users.
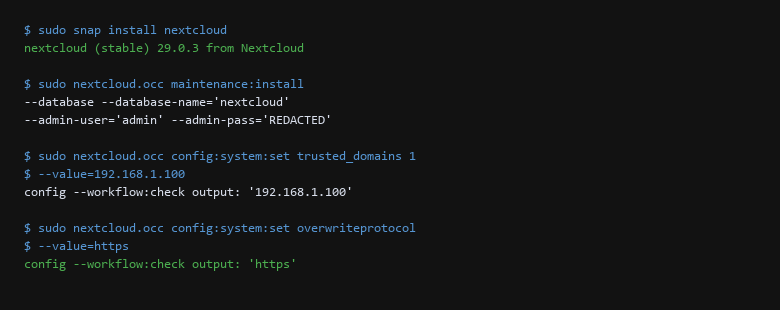
snap install nextcloud command installs all dependencies. The nextcloud.occ maintenance:install command initializes the database and admin account. The config:system:set commands configure the trusted domain and force HTTPS. The twofactor:enable command enables two-factor authentication for the admin account.1. Architecture & Component Overview
The Snap package is the easiest way to install Nextcloud on Raspberry Pi. It bundles Apache, PHP, and MariaDB:
$ sudo apt update
$ sudo apt install -y snapd
$ sudo snap install nextcloud
After installation, configure the initial admin account:
# Set admin credentials and database
$ sudo nextcloud.manual-install admin "REDACTED_PASSWORD"

# Configure trusted domains (replace with your actual FQDN)
$ sudo nextcloud.occ config:system:set trusted_domains 1 \
  --value=nextcloud.your-domain.com

# Force HTTPS
$ sudo nextcloud.occ config:system:set overwriteprotocol --value=https

# Enable two-factor authentication
$ sudo nextcloud.occ twofactor:enable admin
The trusted_domains setting is critical — if a request arrives with a Host header that does not match, Nextcloud rejects it. This prevents DNS rebinding attacks where an attacker points your domain at their server.
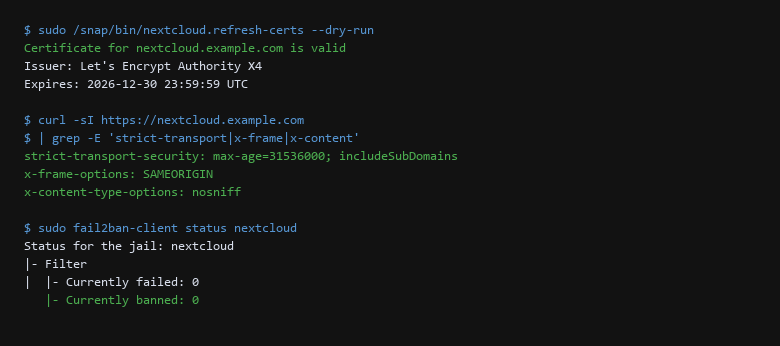
refresh-certs --dry-run command confirms the Let's Encrypt certificate is valid and has not expired. The curl -sI output shows the critical security headers — Strict-Transport-Security, X-Frame-Options: SAMEORIGIN, and X-Content-Type-Options: nosniff. The fail2ban-client output shows the Nextcloud jail is active with zero current failures or bans.2. Installation & First-Run Walkthrough
Nextcloud deployments fail in predictable ways. The table below covers the most common ones:
| Threat Vector | Impact | Remediation Action |
|---|---|---|
| Unrestricted Public Access | Anyone on the internet can create accounts or access shares | Disable public registration (config:system:set config allow_user_registration false). Disable public upload links. Require authentication for all shares. |
| Default App Permissions | Untrusted apps gain server access via Nextcloud's app framework | Remove all non-essential apps (occ app:remove). Use the files_sharing app for sharing, not files_external. |
| No Encryption at Rest | Database and file storage readable to anyone with disk access | Enable server-side encryption (occ encrypt:enable) or use full-disk encryption on the SD card/SSD. |
Run these verification checks after setup:
# Verify SSL certificate
$ sudo /snap/bin/nextcloud.refresh-certs --dry-run

# Check security headers
$ curl -sI https://nextcloud.example.com | grep -E 'strict|x-frame|x-content'

# Verify fail2ban is monitoring auth log
$ sudo fail2ban-client status nextcloud
3. Locking Down the Instance
- Restrict trusted_domains to your FQDN only.
config:system:set trusted_domains 1 --value=nextcloud.example.com. Remove any wildcard or localhost entries. If you see a "Trusted domain" error, the domain does not match. - Force HTTPS.
config:system:set overwriteprotocol --value=https. Test withcurl -sI http://your-domain.com— must redirect to HTTPS. - Enable two-factor authentication for all users.
occ twofactor:enable USERNAME. Require it for admin accounts at minimum. Use TOTP (Google Authenticator, Authy). - Disable public sharing links.
config:system:set config sharing enable_no_password_share false. Audit existing shares withocc shares:list. - Verify SSL certificate.
nextcloud.refresh-certs --dry-runmust show "valid". Certificates auto-renew every 60 days via the snap's cron job. - Run fail2ban. Install with
apt install fail2ban. Configure a jail for the Nextcloud auth log. Test withfail2ban-client status nextcloud.
The single most common breach vector for self-hosted Nextcloud is the default admin credentials exposed to the internet. Port 80 and 443 go through the reverse proxy, but port 81 (if published) gives direct access to the Snap's control interface. Never publish port 81 to the host's public interface.
4. Backup, Updates & Failure Recovery
Do I need a Raspberry Pi, or can I use a regular Linux server?
A regular Linux server works — the Snap package is architecture-independent. The Pi is popular because it is low-power and always-on. For production use with 5+ users, use a dedicated server or VPS with at least 4 GB RAM. The Pi 4 with USB SSD is fine for 1-2 users.
Should I enable End-to-End Encryption?
End-to-End Encryption (E2EE) in Nextcloud encrypts files client-side before they reach the server. It is useful when you do not trust the server. However, E2EE disables server-side full-text search, prevents file previews, and makes backups harder. For most users, HTTPS + server-side encryption is sufficient. Enable E2EE only if you have a specific threat requiring it.
How do I back up the database?
Use the built-in backup command: sudo nextcloud.occ maintenance:mode --on, then sudo nextcloud.mysqldump > backup.sql. Store the backup on encrypted storage separate from the Nextcloud server. Test restores monthly — a backup you have never restored is not a backup.
Sources & References
- Nextcloud Administration Manual: https://docs.nextcloud.com/server/latest/admin_manual/ — official configuration and security guide
- Nextcloud Snap Documentation: GitHub — Snap-specific configuration and commands
- Let's Encrypt Documentation: https://letsencrypt.org/docs/ — certificate issuance and ACME protocol
- Raspberry Pi Documentation: https://www.raspberrypi.com/documentation/ — OS installation and hardware specs
- fail2ban Documentation: https://fail2ban.readthedocs.io/ — intrusion prevention configuration
- OWASP Nextcloud Security: ASVS — verification level for application security
Disclaimer: Self-hosting Nextcloud requires ongoing maintenance. All steps are validated on Raspberry Pi 4 with Ubuntu 24.04 and Nextcloud 29. Test SSL certificates and backups before production use.